AI changes the trust boundary.
Agents introduce new decisions about delegated authority, tool access, and data exposure. Security must follow the action from the model to the API and the business system behind it.
SECURITY STRATEGIST / SPEAKER
Connecting attacker behavior, security architecture, and the decisions that protect a business.
01 / PERSPECTIVE
The most useful security conversation connects a threat to an architectural decision—and that decision to a business outcome.
My focus is on how applications, identities, APIs, and infrastructure interact. Understanding those relationships is what makes it possible to limit exposure, contain an attacker, and keep essential services running.
Agents introduce new decisions about delegated authority, tool access, and data exposure. Security must follow the action from the model to the API and the business system behind it.
Discover what is exposed, understand who can do what, and inspect the business workflow. Valid requests can still produce unauthorized or damaging outcomes.
Visibility, least privilege, segmentation, and DDoS readiness belong in the design. The measure that matters is how well the business operates under pressure.
02 / SPEAKING
Technical substance for practitioners. Clear decisions for executives. Topics built around the threats and tradeoffs your audience faces.
When a model can use tools, the security question becomes what it is allowed to do. Explore prompt injection, excessive agency, API-mediated actions, and the trust boundaries between agents, integrations, and enterprise data.
Audience takeaway A practical way to map agent permissions, validate actions, and place controls where business impact occurs.
For security architects, engineering leaders, and AI teamsModern applications and AI workflows depend on APIs. This session connects discovery, object-level authorization, schema validation, and business-logic abuse to a threat model that reflects the way the application actually works.
Audience takeaway A framework for finding exposed workflows and prioritizing controls across development and production.
For AppSec, platform engineering, and security architecture teamsPrevention is one part of resilience. Connect identity, application access, segmentation, and incident response to the systems the business cannot afford to lose. Examine how architecture shapes lateral movement and recovery.
Audience takeaway A clearer set of priorities for reducing blast radius and validating business continuity.
For CISOs, executive teams, and enterprise architectsAttack volume is only part of the DDoS problem. Explore architectural dependencies, application-layer pressure, provider coordination, and the operational decisions that determine whether an essential service stays available.
Audience takeaway A resilience-oriented approach to testing readiness across enterprise, government, and critical infrastructure.
For infrastructure leaders, security teams, and public-sector audiences03 / SELECTED WORK
Published perspectives and conversations on the systems, assumptions, and decisions behind security.
A conversation about AI agents, API exposure, and evaluating what security tools actually achieve.
API vulnerabilities, attacker behavior, and a layered approach to protecting modern applications.
API discovery, exposed credentials, and cloud automation: why hidden endpoints and shared secrets leave critical workflows vulnerable.
Read the article04 / ABOUT TONY
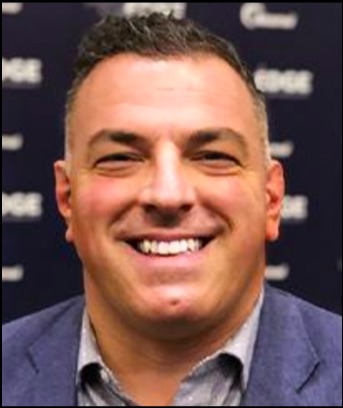
Tony Lauro is Senior Director of Security Technology and Strategy at Akamai Technologies.
His work brings together cybersecurity guidance, architectural analysis, and application and network security. Over more than 25 years, he has worked across finance, healthcare, automotive, enterprise, and mobile applications.
With a background in security operations and enterprise architecture, Tony connects the technical details of an attack to the decisions leaders need to make. His focus spans AI and API security, Zero Trust, segmentation, and resilient Internet-facing systems.
Brazilian Jiu Jitsu, skateboarding, and filmmaking. Different disciplines. The same curiosity.
LET’S CONNECT
For speaking, executive discussions, and professional connections, reach out on LinkedIn.